Showing posts with label CCNA. Show all posts

How to configure dynamic nat in cisco router using packet tracer step by step guide


How To Configure Dynamic NAT in Cisco Router | In this article we will learn what is dynamic  nat , how to configure dynamic  nat and after configuring verify the dynamic  nat in cisco router using packet tracer software.

Suppose in an organization we have reserved private network (192.168.1.0/24) to use to communicate among the users. If all users want to access to the internet then dynamic nat plays an important role to fulfill this requirement.

Private ip address Range

Class A => 10.0.0.0  to 10.255.255.255
Class B => 172.16.0.0 to 172.31.255.255
Class C=> 192.168.0.0 to 192.168.255.255

 Type of NAT

Three types of nats are available.


What is Dynamic NAT

In the dynamic nat router is configured a pool of ipv4 address . when user want to access to internet then node request to router to mapping public ip address to the corresponding private ipaddress. 

Lab Diagram
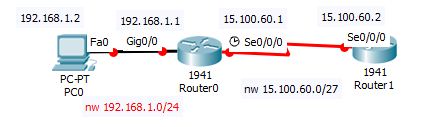
 
How to configure dynamic  nat in cisco router using packet tracer
                           How to configure dynamic  nat in cisco router using packet tracer
In the above diagram we configure dynamic nat in cisco router using packet tracer software.

Configuration of dynamic nating

To configure dynamic nat below some steps we have to follow.

  1. Create a pool of public ip addresses to the router to map the private ip addresses.
  2. Create an access list to permit ip addresses which to be translated.
  3. Map the pool to the access list.
  4. Finally apply nat configuration  to the router interface.

In  the above diagram we have a private network 192.168.1.0/24 which to be mapped to public network which is 15.100.60.0/27. To configure it we follow the below steps.

Router(config)#ip nat pool mypool 15.100.60.3 15.100.60.30 netmask 255.255.255.0
Router(config)#ip access-list extended mypool
Router(config-ext-nacl)#permit ip 192.168.1.0 0.0.0.255 any
Router(config-ext-nacl)#exit
outer(config)#ip nat inside source list mypool pool mypool
Router(config)#int gig0/0
Router(config-if)#ip nat inside
Router(config-if)#exit
Router(config)#int se0/0/0
Router(config-if)#ip nat outside
Router(config-if)#exit
Router(config)#

verify of dynamic nating

After configuring dynamic nating we need to verify it. To verify it we execute the below command.

Router#sh ip nat statistics
Total translations: 0 (0 static, 0 dynamic, 0 extended)
Outside Interfaces: Serial0/0/0
Inside Interfaces: GigabitEthernet0/0
Hits: 0 Misses: 0
Expired translations: 0
Dynamic mappings:
-- Inside Source
access-list mypool pool mypool refCount 0
pool mypool: netmask 255.255.255.0
start 15.100.60.3 end 15.100.60.30
type generic, total addresses 28 , allocated 0 (0%), misses 0

If this article is helpful to know about How To Configure Dynamic NAT in Cisco Router please share and subscribe this article.


Please Donate To Bitcoin Address: [[address]]
Donation of [[value]] BTC Received. Thank You.
[[error]]
How to configure enable/secret password of cisco router step by step guide


How to configure enable/secret password of cisco router

In this article we learn how to setting enable password of the cisco router. Different types of password you can configured to access the cisco router such as enable password ,secret password, for ssh connection and so on.

Set up enable password of cisco router for demo

To secure a router we configure enable password. It uses to move the mode from user execution mode to privileged execution mode and as well as we can access global configuration mode using enable password.

To configure the enable password of the cisco router we execute the  below command .

Router>en
Router#conf t
Enter configuration commands, one per line. End with CNTL/Z.
Router(config)#enable password cisco

After execution the above command we create the enable password of the cisco router which is stored in the config file of the router. To find the line from the config file we execute the below command.

Router>en
Password:
Router#show running-config | include enable
enable password cisco

We saw fom the above output that the stored password is in plain text it is not a encrypted format .anyone can read the the stored password from the config file because it is in plain text.

To overcome the problem create a new type of password called secret password .it is not in plain text it is stored in the configuration file in encrypted format which is not readable from anyone .

 Set up secret password of cisco router for demo

To overcome the problem create a new type of password called secret password .it is not in plain text it is stored in the configuration file in encrypted format which is not readable from anyone . when we configure secret password it take over the responsibility to move the mode from user execution mode to privileged execution mode. To configure the secret password we execute the below command.

Router#conf t
Enter configuration commands, one per line. End with CNTL/Z.
Router(config)#enable password cisco
Router(config)#enable secret cisco123

Note: you can not use same password in the secret password which you use to create enable password.

To view the configuration file we execute the below command.
Router>en
Password:
Router#
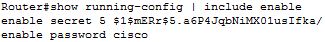
Router#show running-config | include enable
enable secret 5 $1$mERr$5.a6P4JqbNiMX01usIfka/
enable password cisco

How to configure enable/secret password of cisco router


In next article we learn how to reset enable password of the cisco router with practical demotration.


Explain brief Introduction of Administrative Distance of router with practical example


Explain brief Introduction of Administrative Distance of router with practical example

In this article we learn what is administrative distance , How is impact the routing decision and default Administrative value of routing protocols.

What is Administrative Distance

Administrative distance is the feature of all routers to select the best trusted route when two or more different routes are there to reach the same destination. Administrative Distance number always in between 0 to 255.

Default Administrative Distance value of different routing protocols

For IGRP Administrative Distance value is 100
For EIGRP Administrative Distance value is 90
For RIP Administrative Distance value is 120
For OSPF Administrative Distance value is 110
For ISIS Administrative Distance value is 115
For STATIC ROUTE Administrative Distance value is 1
For DIRECTLY CONNECTED ROUTE  Administrative Distance value is 0

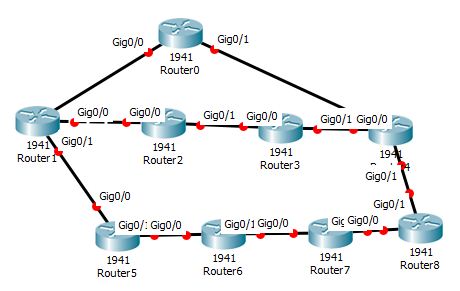
Sample diagram to explain Administrative Distance

 
Explain brief Introduction of Administrative Distance of router with practical example
Explain brief Introduction of Administrative Distance of router with practical example
Suppose route1 wants to reach to router4.To reach the router4 there are 3 possible route.
One is router1=>router0=>router4
Second is router1=>router2=>router3=> router4
And third is router1=>router5=>router6=>router7=>router8=>router4.
First route takes 2 hops to reach router4.Second route takes 3 hops to reach route4 and third route takes 5 hops to reach router4.
If we taken rip protocol we know that rip is calculate its best route using hop counts. Least hop count consider as the best route among the three. Here route one is the best route for the rip protocol.
For ospf and eigrp bset route is calculated using band width. if first route has band width  3mbps,second route has bandwidth 4mbps and third route has band width of 8mbps,then eigrp and ospf takes third route to reach the destination.
When network admin configure static route he/she decides the best route among the three. Suppose here network admin select second route to reach the destination.
Now router have consider best trusted route using the administrative distance. In the above scenario router select second route to reach the destination as static route has administrative distance which is 1.


How to reset forgot enable password of cisco router with practical demo step by step


How to reset forgot enable password of cisco router with practical demo

In this article we learn if we forgot enable password of cisco router how to reset it successfully. It is very common trouble shooting of a network administrator. To secure cisco router we use enable password .it uses to move the user execution mode to privileged execution mode. 

When we enter wrong password  we got the below error.

Router>en
Password:
Password:
Password:
% Bad secrets

How to reset forgot enable password of cisco router with practical demo

Note: after enter three times wrong password we got the above error.
To break the router password we follow the below steps.

Show the current IOS version  of router

 First we have to note down the current IOS register version of the router to do this we execute the below command.
 Router>show version
Current version is 0x2102

Boot the route in ROMMON mode


In the second step we boot the router in ROMMON mode .to boot in the ROMMON mode switch off the router we it is booting up press “ctrl+c” to enter the ROMMON mode.

Change the configure register version


After enter the ROMMON mode we need to change config register version to 0x2142 and then reboot the router.

ROMMON> confreg 0x2142
ROMMON>reset


After change the config register router bypass the startup configuration where password is stored.

Copy startup config to running config


After that copy startup config to running config. To do this we execute the below command.

Router# copy startup-config running-config

Reconfigure the enable password


Now reconfigure the enable password . to configure it  visit this below reference


change the original version of configuration register 
Now we need to change the original version of configuration register that is 0x2102.to do this we need to enter config mode and execute the below command.

Router(config)# config-register 0x2102

Now save the configuration and reboot the router .
After doing all the steps we reset the forgot enable password of the cisco router.

HOW TO CONFIGURE EIGRP ON CISCO ROUTER USING PACKET TRACER SOFTWARE STEP BY STEP GUIDE


HOW TO CONFIGURE EIGRP ON CISCO ROUTER USING PACKET TRACER SOFTWARE

In this article we learn how to configure EIGRP and how to verify EIGRP after configuration on cisco router using packet tracer software.

What is EIGRP

EIGRP is called  advanced distance vector and it is  classless protocol. It is a standard protocol and use for cisco and non cisco device, but initially it was cisco proprietary.  It is included all features of igrp. It supports upto 255 hop count and by default it supports upto 100 hop count.

Administrative distance of EIGRP is 90.It does not uses broadcast address .It only uses multicast and unicast address.

By default EIGRP uses bandwidth and delay to calculate the metric calculation.

Lab diagram

HOW TO CONFIGURE EIGRP ON CISCO ROUTER USING PACKET TRACER SOFTWARE

               HOW TO CONFIGURE EIGRP ON CISCO ROUTER USING PACKET TRACER SOFTWARE


In the above diagram we learn the configuration of EIGRP on cisco router using packet tracer software.

Configuration of EIGRP on cisco router using packet tracer

We have to follow two commands to configure EIGRP on cisco router. To enabling the EIGRP we use “router eigrp <AS NO>” (AS is the autonomous system no which should be same ,if as no is different routers can not build eigrp neighbour relationship). Secondly router has to advertise their network to configure the EIGRP.

For router0
#router eigrp 1
#network 10.0.0.0
#network 172.16.0.0


For router1

#router eigrp 1
#network 172.16.0.0
#network 192.168.1.0

verify of EIGRP on cisco router using packet tracer

After configuration we need to verify the configuration whether it is configured successfully or not. To verify the the neighbour table on the router0 we execute the below command.

Router#show ip eigrp neighbors
IP-EIGRP neighbors for process 1
H Address Interface Hold Uptime SRTT RTO Q Seq
(sec) (ms) Cnt Num
0 172.16.0.2 Se0/0/0 13 00:00:42 40 1000 0 4

To verify the topology table from the router0 we execute the below command.

Router#sh ip eigrp topology
IP-EIGRP Topology Table for AS 1/ID(172.16.0.1)

Codes: P - Passive, A - Active, U - Update, Q - Query, R - Reply,
r - Reply status

P 10.0.0.0/8, 1 successors, FD is 5120
via Connected, GigabitEthernet0/0
P 172.16.0.0/16, 1 successors, FD is 2169856
via Connected, Serial0/0/0
P 192.168.1.0/24, 1 successors, FD is 2172416
via 172.16.0.2 (2172416/5120), Serial0/0/0

To verify the routing table from router0 we execute the below command

Router#sh ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2, E - EGP
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
* - candidate default, U - per-user static route, o - ODR
P - periodic downloaded static route

Gateway of last resort is not set

10.0.0.0/8 is variably subnetted, 2 subnets, 2 masks
C 10.0.0.0/8 is directly connected, GigabitEthernet0/0
L 10.0.0.1/32 is directly connected, GigabitEthernet0/0
172.16.0.0/16 is variably subnetted, 2 subnets, 2 masks
C 172.16.0.0/16 is directly connected, Serial0/0/0
L 172.16.0.1/32 is directly connected, Serial0/0/0
D 192.168.1.0/24 [90/2172416] via 172.16.0.2, 00:04:12, Serial0/0/0

Thanks for learning this article. If you like this article please like ,share and comment for this article.   

Please Donate To Bitcoin Address: [[address]]

Donation of [[value]] BTC Received. Thank You.
[[error]]

Intoroduction of EIGRP and how EIGRP works


Intoroduction of EIGRP

In this article we learn about the feature of EIGRP ,how EIGRP works and in the next part we learn the configuration of EIGRP for demotration purpose using packet tracer software.

Feature of EIGRP

EIGRP is called  advanced distance vector and it is  classless protocol. It is a standard protocol and use for cisco and non cisco device, but initially it was cisco proprietary.  It is included all features of igrp. It supports upto 255 hop count and by default it supports upto 100 hop count.

Administrative distance of EIGRP is 90.It does not uses broadcast address .It only uses multicast and unicast address.

By default EIGRP uses bandwidth and delay to calculate the metric calculation.

Type of EIGRP table

There are three types of tables which EIGRP protocol uses.
·         Neighbour table

To show the neighbour table we use the below command.
#show ip eigrp neighbour

·         Topology table

To show the topology table we use the below command.
#show ip eigrp topology

·         Routing table.

To show the routing table we use the below command
#show ip route


How EIGRP works

In this section we learn how to EIGRP works.
Suppose we have two routers.

STEP1: when router1 is advertising its interface then it send a hello packet to router2 using 224.0.0.10 multicast address. Router2 can not understand the the message unless it advertise its interface. After router2 advertises ites interface it also send a hello message to router1 using unicast address. After exchanging hello messages they build a neighbour table.

STEP2:  After established the neighbour table they exchange their routing information to each other and select the all best path and build a topology table.

STEP3:  After completing step2 they chose the top best route among the best routes and build a routing table.

Intoroduction of EIGRP

                                       Intoroduction of EIGRP


How to configure nat overload in cisco router using packet tracer step by step guide


In this article we will  learn what is  nat overload(PAT), how to configure  nat overload in cisco router using packet tracer software.

Normally we use private ip inside the organization which is not allow to users to access the internet,then we use dynamic nat to fulfill our purpose. If ISP not provides organization pool of ip address then we go the another option which is called NAT overload(PAT).

Private ip address Range

Normally we use private ip address which is reserved inside the organization to communicate internal purpose which is not public ip address. The ange are given below.

Class A => 10.0.0.0  to 10.255.255.255
Class B => 172.16.0.0 to 172.31.255.255
Class C=> 192.168.0.0 to 192.168.255.255

Type of NAT

Three types of nats are available.


What is NAT overload

In the dynamic nating we saw that ISP provides us a pool of public ip address to map with internal private ip to access internet. If ISP gives us few public ip addresses or 1 public ip address instead a pool of public ip addresses to map internal private ip addresses to access internet. In this scenario NAT overload is configured to overcome the problem.

Lab Diagram

How to configure nat overload in cisco router using packet tracer

                         How to configure nat overload in cisco router using packet tracer


In the above diagram we configure nat overload in cisco router using packet tracer software.

Configuration of NAT overload(PAT)

If ISP gives us few ip addresses or even 1 ip address so we can eliminate the netmask keyword from the dynamic nating command.

Router(config)#ip nat pool mypool 15.100.60.3 15.100.60.4
Router(config)#ip access-list extended mypool
Router(config-ext-nacl)#permit ip 192.168.1.0 0.0.0.255 any
Router(config-ext-nacl)#exit

Here we use only two public ip addesses to map with the internal private ip addresses.Finally we bind the access list with pool and use overload keyword end of the command.

Router(config)#ip nat pool inside source list mypool pool mypool overload


In this article we have   learned what is  nat overload(PAT), how to configure  nat overload in cisco router using packet tracer software.


How to configure static nat in cisco router using packet tracer step by step guide


Static Nat Configuration | In this article we learn what is static nat , how to configure static nat and after configuring verify the static nat in cisco router using packet tracer software.

What is NAT

Two types of ip address are available in the network terminology. one is public address and other is private address. In an organization internal network should use private ip address to communicate each other ,normally is called LAN. These ip addresses not used for the internet .They can not connect to the internet .To overcome the limitation NAT is come to play is vital role .private ip address is mapped to the public ip address to communicate to the internet  and its hide the private ip address.  

Type of NAT

Three types of nats are available .

Static nat: static nating is the type of nat where one private ip is mapped to the public ip address.This is basically use when we are going to host webserver publicly.

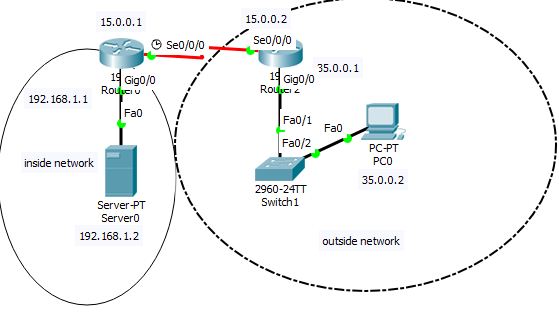
Lab Diagram

 
How to configure static nat in cisco router using packet tracer,Static Nat Configuration
Static Nat Configuration

          How to configure static nat in cisco router using packet tracer


In the above diagram we configure static nat in cisco router using packet tracer software.

Static Nat Configuration

In the internal network we have one web server with private ip address 192.168.1.2 and its gateway is 192.168.1.1 which is configured in the router gig 0/0 interface .In the above diagram there is another network which is 15.0.0.0/8 and there is another network which is 35.0.0.0/8 both two networks  are public.


We are going to mapping web server private ip (192.168.1.2) to public ip (15.0.0.3).
To configure it we need to execute the below steps.

Router>en
Router#conf t
Enter configuration commands, one per line. End with CNTL/Z.
Router(config)#ip nat inside source static 192.168.1.2 15.0.0.3
Router(config)#int gig0/0
Router(config-if)#ip nat inside
Router(config-if)#exit
Router(config)#int se0/0/0
Router(config-if)#ip nat outside
Router(config-if)#exit

We have configured static nat to execute the above commands.

 Verify  of static nating

After configured static nating we need to verify it whether it is configured or not.To verify it we ping the webserver from the outside network.
Before configure static nat when we going to ping the webserver from the outside network it get the following output.

Packet Tracer PC Command Line 1.0
C:\>ipconfig

FastEthernet0 Connection:(default port)

Link-local IPv6 Address.........: FE80::290:21FF:FE1D:19C0
IP Address......................: 35.0.0.2
Subnet Mask.....................: 255.0.0.0
Default Gateway.................: 35.0.0.1

C:\>ping 192.168.1.2

Pinging 192.168.1.2 with 32 bytes of data:

Request timed out.
Reply from 192.168.1.2: bytes=32 time=22ms TTL=126
Reply from 192.168.1.2: bytes=32 time=16ms TTL=126
Reply from 192.168.1.2: bytes=32 time=15ms TTL=126

Ping statistics for 192.168.1.2:
Packets: Sent = 4, Received = 3, Lost = 1 (25% loss),
Approximate round trip times in milli-seconds:
Minimum = 15ms, Maximum = 22ms, Average = 17ms

After configure static nat when we going to ping the webserver from the outside network it get the following output.

C:\>ping 192.168.1.2

Pinging 192.168.1.2 with 32 bytes of data:

Reply from 15.0.0.3: bytes=32 time=17ms TTL=126
Reply from 15.0.0.3: bytes=32 time=11ms TTL=126
Reply from 15.0.0.3: bytes=32 time=23ms TTL=126
Reply from 15.0.0.3: bytes=32 time=17ms TTL=126

Ping statistics for 192.168.1.2:
Packets: Sent = 4, Received = 4, Lost = 0 (0% loss),
Approximate round trip times in milli-seconds:
Minimum = 11ms, Maximum = 23ms, Average = 17ms

We execute another command to verify the static natting.

Router#sh ip nat translations
Pro Inside global Inside local Outside local Outside global
--- 15.0.0.3 192.168.1.2 --- ---
tcp 15.0.0.3:80 192.168.1.2:80 35.0.0.2:1025 35.0.0.2:1025
tcp 15.0.0.3:80 192.168.1.2:80 35.0.0.2:1026 35.0.0.2:1026

If this article is helpful to know about Static Nat Configuration please share and subscribe this article.